

Introduction
The REST Call action allows you to send HTTP calls to a REST API while a process is running.
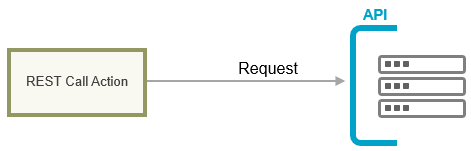
The response—or the result of the REST call—is retained in the processing context (SharedState) for further processing.
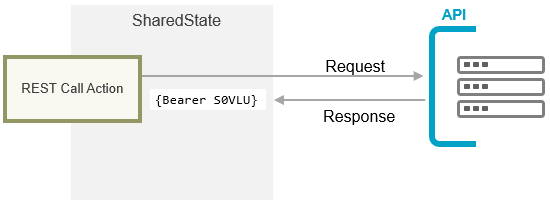
You can include as many REST call actions as you like in a process. This allows you to access the values returned in the response. This allows you, for example, to retrieve the authentication data in an initial REST call so that you can then send the next request in the subsequent REST call.
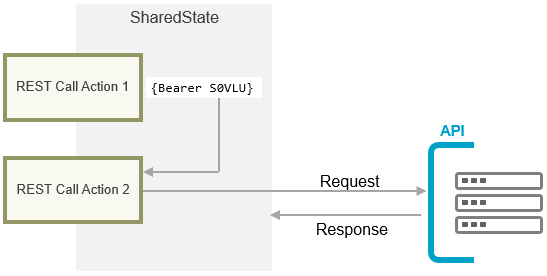
In addition to the ability to access the processing context via REST calls, you can also use the standard Groovy methods for this purpose. For more information on this topic, see the following link : Class SharedState.
Dialog-Based Data Collection - REST API Client
In the REST call action, you can enter all the information required for the REST call using a dialog box. You will be guided through a series of dialog boxes in which you will be asked to provide the necessary information.
(In the background, Apache HTTP Client 5 acts as a REST API client.)
Dynamic REST Call Actions - Resource Mapping
"Resource mapping" is available within each REST call action. With its help, you can make REST call actions dynamic or variable in virtually any way. You can do this by inserting placeholders into the REST call action that can be populated from various sources. When the REST call is executed, the placeholders are populated with the values determined at the time of execution. Values can be obtained from the following sources at the time the REST call is executed:
-
Static Text
-
Request
-
Processing Context (SharedState)
-
Data Group
-
System Data Group (System Data Group)
-
User Rating
-
Previous Request (Previous REST Call Action)
-
Login Information Store (Login Information Store)
-
Parameter Memory (Parameter Memory)
For detailed information on this topic, see the " Resource Mapping" section.
Authentication Options
The following authentication options are available for REST calls:
-
Basic Authentication
-
Authentication via API Key
-
Authentication via Bearer Token
In addition, you can create your own authentication methods.
If an API issues session cookies, these can be stored and reused in subsequent REST calls made by the same process.
The following section provides an overview of the steps you need to take when creating a REST call action: