

Scenario 5 - Encrypted Connection for Internal Intrexx Communication via REST
Architecture
In the context of the REST API, two components are relevant in Intrexx: Intrexx Portal Manager and Portal Servicee)
The portal has its own web server on which the REST API runs. The portal uses certificates for communication. The Portal Manager connects to the portal service.
Certificate Types
CA-Signed Certificates If you are using a CA-signed certificate, you do not need to take any special action other than renewing your certificate when it expires (see below).
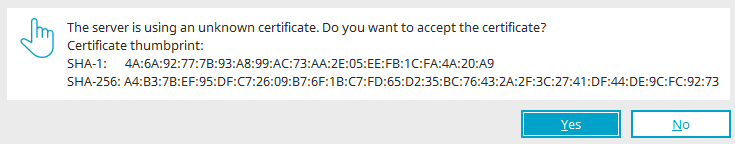
Self-Signed Certificates If you use a self-signed certificate, you must confirm (once) when starting the Portal Manager that you trust the certificate. If you generate the self-signed certificate through Intrexx (see below), it is valid for three years.
Please note that CA-signed certificates (public or private) are preferable to self-signed certificates. For one thing, they are less prone to errors, and for another, they are better suited to the requirements of a public-key infrastructure.
Renew Certificates
You may need to renew or replace your certificate. This may be the case, for example, if your certificate has expired or if the URL or IP address for which your certificate was issued has changed.
The script is located in the directory <installation directory>/bin/<operating system>/createcertificate
The script can be run with the following parameters:
-h, --help: Opens a help text in the console
-p, --portal: If a certificate is to be replaced for a portal, the portal directory must be specified here.
An example of how to run the script to replace a portal certificate might look like this: createcertificate.sh -p /opt/intrexx/org/portal --san dns:www.example.org ip:127.0.0.1