

When connecting Intrexx to third-party systems, it is important to distinguish whether Intrexx is consuming or providing data. When Intrexx consumes data—that is, when it acts as a client—only a certificate with a public key needs to be stored in Intrexx. If Intrexx provides data—that is, acts as a server—a certificate containing a public and private key must be stored in Intrexx.
Consume data
Intrexx offers integrations with numerous third-party systems.
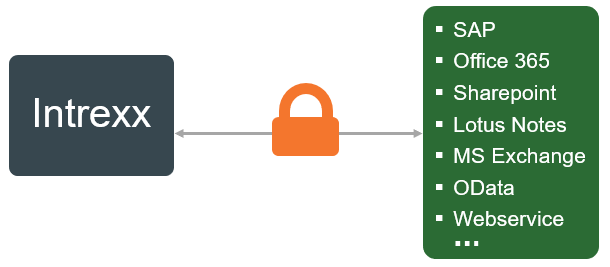
To establish an encrypted connection to these systems, you need a certificate from the operators of the third-party systems that contains the public key.
You must save this in your portal's central certificate store.
Note: By default, the central certificate store contains a number of certificates from trusted certification authorities. These are shipped with the JDK included in Intrexx. Therefore, with common third-party systems hosted in the cloud, it is possible that the certificate is already present in the central certificate store.
Step-by-step guide
To import a certificate into your portal's certificate store, follow these steps:
-
Open the portal properties ("Portal > Portal Properties").
You will be taken to the "Edit Portal pagee.
-
Click "Certificates."
You will be taken to the "Certificates" page.
The lock icon and the link will only appear if you have not yet accessed the certificate store during the current session.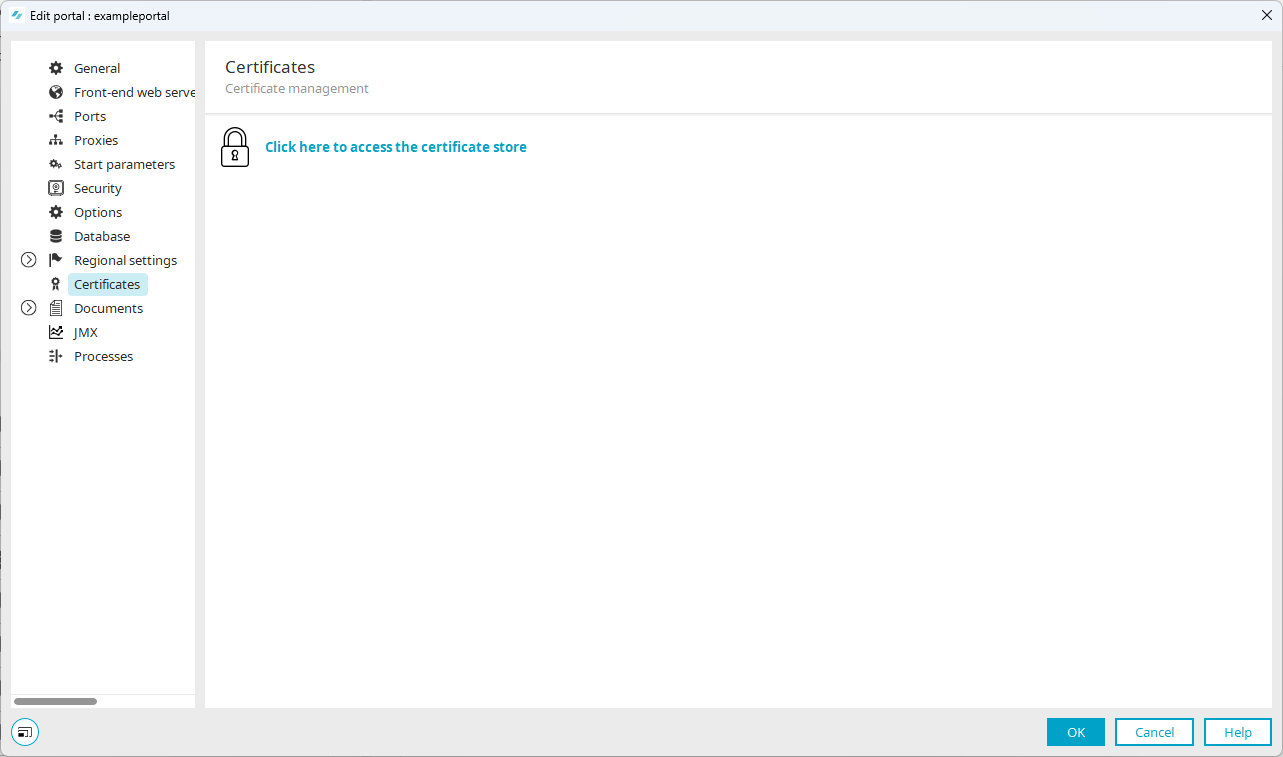
-
Click here to access the certificate store.
The "Certificate Store Password" dialog box will appear.
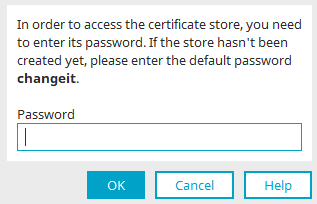
Enter "changeit" as the password if you have not yet set a password for the certificate store. (You can change the password for the certificate store in the next dialog.)
Enter your own password if you have set one for the certificate store.
-
Click "OK."
You will now see a list of all certificates included with Intrexx.
-
Make the necessary entries.
-
Click "Next."
Details of the certificate selected in the previous step are shown in the next dialog. -
Click "Next."
-
In the next dialog box, enter an alias name for the certificate.
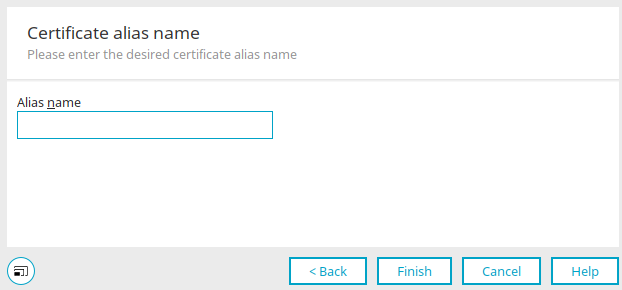
The alias name helps you identify the certificate in the certificate store. -
Click "Finish."
You will now be returned to the certificate store. The certificate you imported will be displayed.
You have imported a certificate into your portal's certificate store.
Click on ""+"".
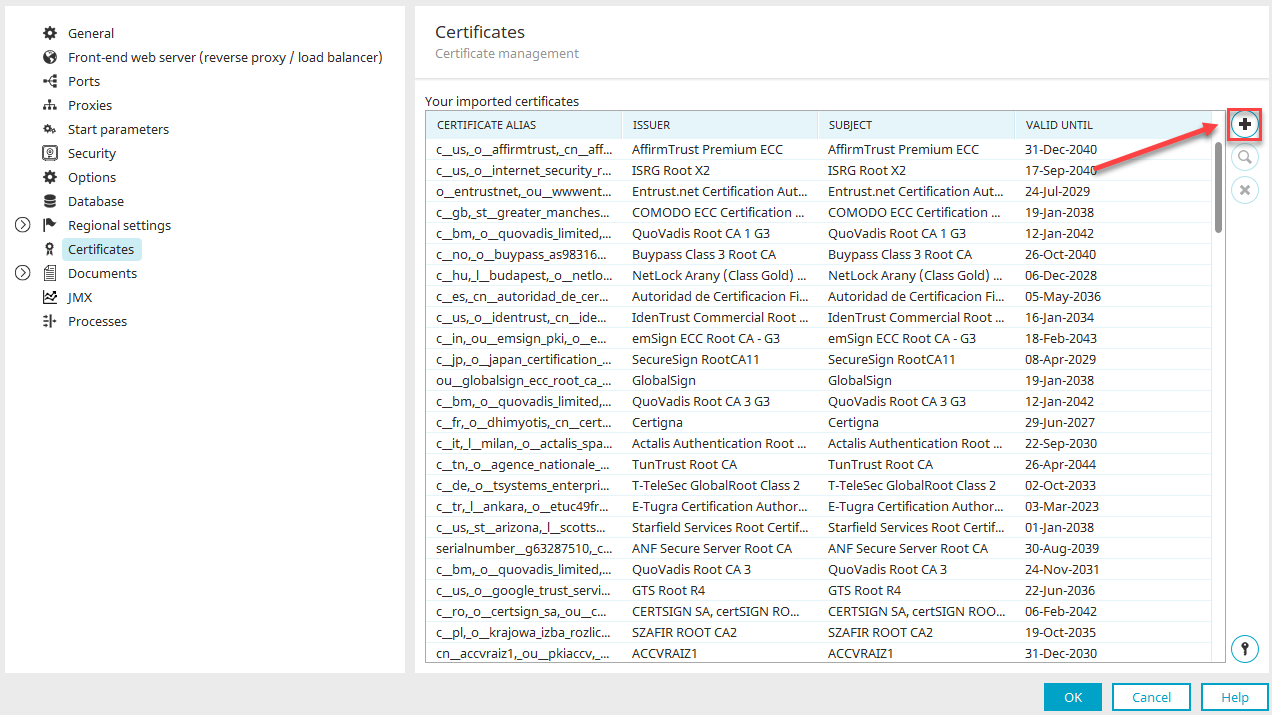
This will take you to the "Certificate Import" dialog box.
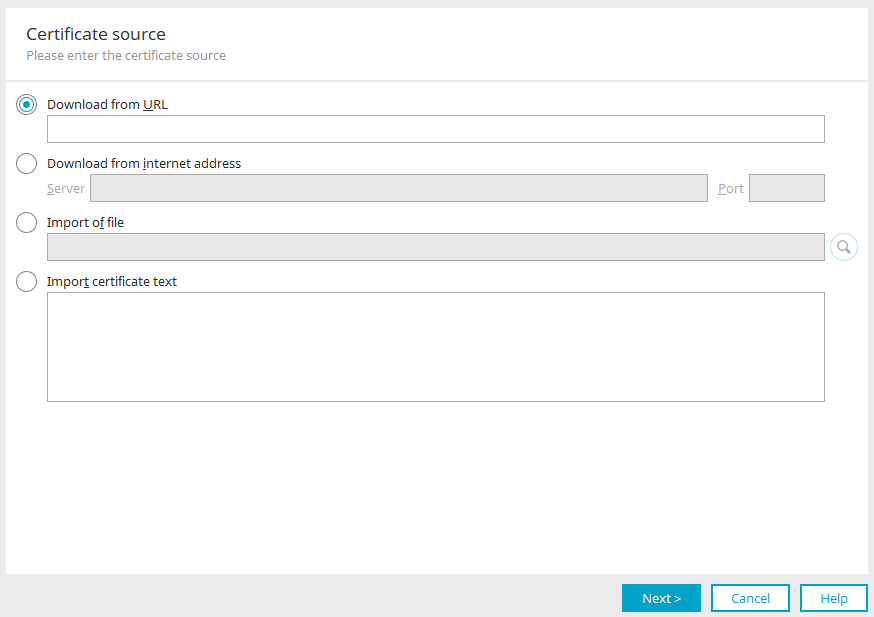
|
Name |
Description |
|---|---|
|
Download from URL |
A certificate can be loaded here. Enter the appropriate URL. |
|
Download from Internet address |
Allows you to download certificates. |
|
Server / Port |
Enter the download server (its name or IP address) and the port. |
|
Import the file |
A certificate file can be integrated with this option. |
 Add File |
Opens a dialog where the certificate file can be selected. |
|
Importing the Certificate Text |
Allows for the direct import of certificate texts. Paste the appropriate text into the input field. |
Reset certificate store
If you no longer remember the password for the certificate store (Portal > Portal Properties > Certificates), you must reset the certificate store. (You cannot "reset" your password.)
To reset the certificate store, replace your portal's certificate store at the file level with the certificate store that was delivered with Intrexx.
You can find your portal's certificate store here:
<intrexx-installation-directory><org><portalname>/internal/cfg/cacerts
You can find the certificate store that was delivered with Intrexx here:
<intrexx-installation-directory>/orgtempl/blank/internal/cfg/cacerts
Please note that any certificates you have added will be lost when the certificate store is reset.
Provide Data
Intrexx can provide data for OData (and web services).
In this case, you'll need to manually create your own keystore and save the certificate—along with the public and private keys—in it.
To make data available via OData, Intrexx uses "Jetty." The keystore must be stored in the Jetty web server.
For more information about "Jetty," please visit the following link: https://www.eclipse.org/jetty/